ShareFile Security: Building Layers of Protection Around Business Data
Share the article
ShareFile for Your Firm
Secure document workflows your team and clients will actually use
Get StartedKey Takeaways
Just as organizations implement operational processes to help protect important assets, Progress ShareFile programs also benefit from monitoring, alerting and response procedures.
Let’s explore how common physical protection concepts can be translated into modern file-sharing and collaboration environments.
(Disclaimer: Not all features inside Progress ShareFile are mandatory, and the more advanced options are only available in higher tier products. Please visit https://www.sharefile.com/plans for a quick overview.)
(Disclaimer 2: The storytelling is only an example scenario. All measures explained can be applied in any high-security environment.)
Important: This article provides a high-level overview of capabilities available within Progress ShareFile. It is intended for informational purposes only and does not constitute comprehensive compliance, or architectural disclosure. Official documentation, certifications and audit reports are available through the Progress ShareFile Trust Center and other approved channels, which may require appropriate authorization or NDA coverage.
The Story:
Many high-security facilities rely on layered physical safeguards, controlled access, monitoring and compartmentalization to protect valuable assets.
Digital Protection Practices
For organizations managing sensitive corporate files, legal documentation or healthcare records, building a physical fortress is impossible. However, building a digital one is within reach.
1. Certified Cloud Architecture
In a high-security facility, many rely on nature’s strongest foundation: A solid bedrock. This helps prevent any possibility of subterranean tunneling or structural undermining.
In the cloud ecosystem, your data must reside on an equally unyielding structural foundation. Progress ShareFile software replaces physical granite with highly audited infrastructure hosted within globally certified cloud environments, validated against elite compliance frameworks including SOC 2 Type II and ISO 27001.
2. 256-Bit Cryptographic Seals
To enter, you won’t pass through a hinged door. Instead, you face a 90-ton rotating steel cylinder. When shut, it rotates slightly into its frame, creating an airtight and watertight seal.
Progress ShareFile software replicates this using 256-bit AES encryption, TLS protocols, HMAC verification and secret-key validation. Cryptographic controls are used to support data integrity by helping identify instances where data may have been modified or can’t be securely validated.
3. Multi-Factor & Identity Authentication
Access to sensitive areas often requires multiple levels of authorization. Entry requires a Control Group, for example three distinct people from separate departments.
Progress ShareFile software provides a modern Rule of Three through multi-factor authentication (MFA) and advanced authorization workflows, strict lockout policies and eIDAS-supported Advanced and Qualified Electronic Signatures (AES/QES).
4. Permissions and Client Portals
Sensitive physical assets are frequently separated into restricted areas with independent access controls, each locked with double combinations and auditor seals.
Progress ShareFile software mirrors this through Granular Access Controls and branded Client Portals. External clients see only assigned folders, supported by isolated permissions, unique per-file encryption keys and robust audit telemetry.
5. Digital Security Options
Upon entering the facility, you will be asked for an identification document and a fingerprint match.
Progress ShareFile software mirrors this with the option to enable MFA where you both need your username and password, as well as an additional identification method, be it phone, SMS or an already installed authentication app on your device.
Note: For certificates and documents regarding cybersecurity, please visit trust.sharefile.com.
Let’s now list the possibilities to harden your environment, and a quick look at how to configure them.
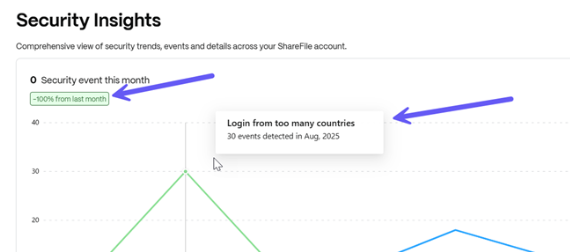
Security Insights
We will start with the Security Dashboard. This is your central administrative view, where related events and trends can be reviewed and investigated.
Suspicious activity, as defined by yourself, will be displayed and easily accessible to take the needed actions.
Antivirus
We’ve all been there, secure environments where you don’t just walk in with your belongings. There’s a line, with a belt, with a machine. It X-rays the content of all the bags, packages or pieces of luggage you carry with you.
Progress ShareFile software does the same for you (automatically) or when you use ShareFile with your on-premises storage, through ICAP.
You can harden the strictness of the AV according to your needs, with the following parameters*:
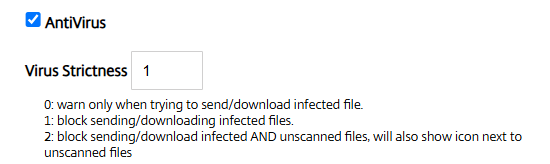
(*Please contact the support team to change the setting.)
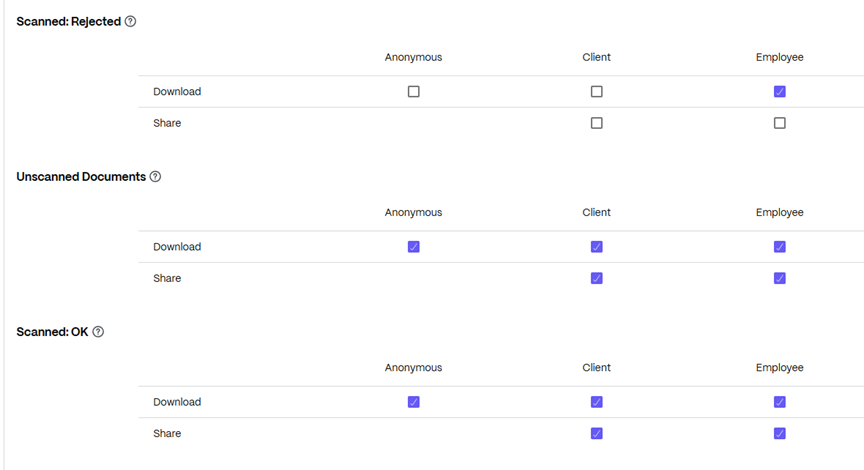
Data Loss Prevention
Available for customers who use their own storage zone controller, you can select how thorough you scan and report your files content. Just as in the real world, these scanners are third-party (hence only available when you have a storage zone controller), but you can allow or restrict certain people and/or “items” from being considered flagged.
Sign-in Policy
Ever walked into a government facility with an employee badge and maybe later with a visitor badge? Or do you know people who’ve been through those different processes?
Same goes for your Progress ShareFile setup. You can allow and deny multiple methods of signing in, make it easier or make it harder if you want.
Let’s cover a couple of options:
Let’s begin with the easiest, used on most platforms: Username/Password.
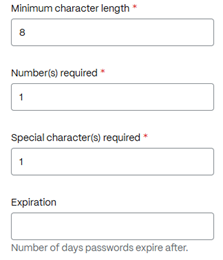
Even though this is not used at a physical location (for obvious reasons), we should bring in the password. Passwords have length, given only to an authorized person and expires after a while.
More secure however is Multi-Factor Authentication.
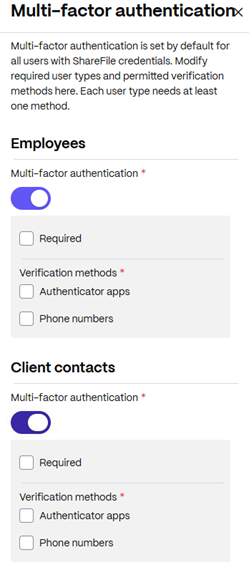
We’ve touched on this topic a bit before, but repeating guidelines never hurts.
There’s, of course, also the possibility that you work together with instances which you trust. Organizations sometimes establish trusted identity relationships with external partners. Similar concepts can be implemented through identity federation and SSO technologies.
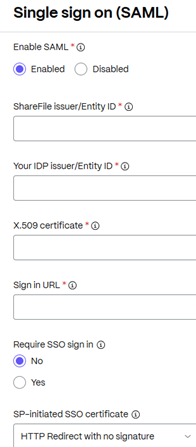
Let’s move on and take a look at how to secure the login for our internal employees. At the physical institution, we have a badge which is connected to the central system. With Progress ShareFile software, you can set up your SAML in order to achieve the same.
As you can see below, the configuration is pretty straightforward. You create a virtual corridor with two doors: one being your ShareFile ID, one being your Authenticator (EntraID for example).
You give the paths, the keys and the type of key (HTTP/HTTPS), and you open the login possibility.
Additional Options
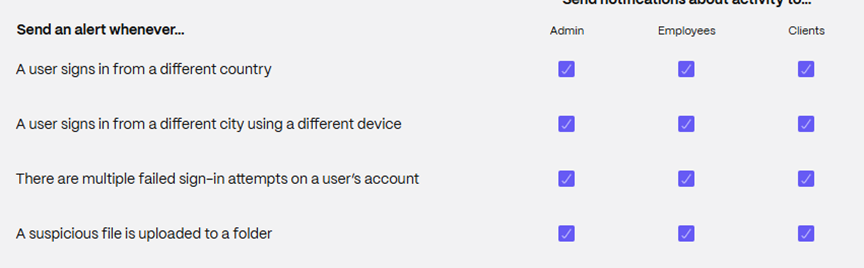
Security measures might change a bit over time, so also in Progress ShareFile software, you can mitigate ad-hoc changes.
Trusted Domains, as an example: you can specify which companies’ domains you trust.
Parameters look as follows:
For additional reporting, you can also configure one of our available SIEM integrations (ShareFile Enterprise and above) and/or configure your SCIM.
And oh, one more thing.
Do you know this?
If you handle documents which may not be disclosed, enable our Watermarking option when sharing:
In the example above, following dynamic text is enabled:
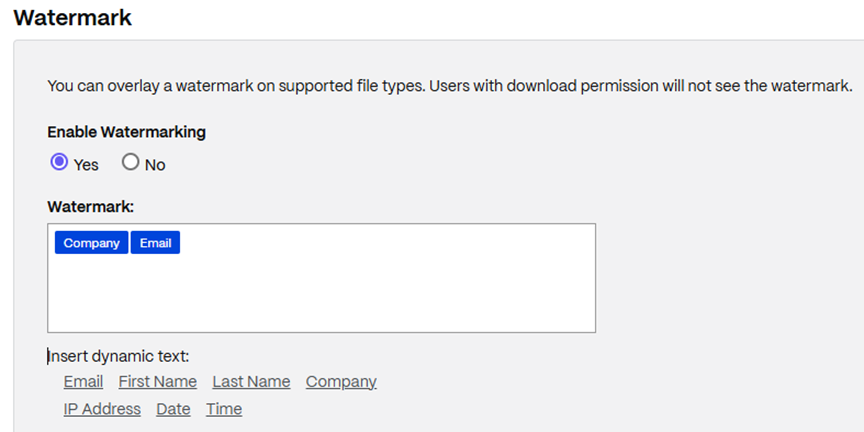
Even though you might not prevent your recipient from screenshotting or taking pictures of your document, the dynamic texts you select will be included.
And now, really, the last remark:
Just as organizations implement operational processes to help protect important assets, our programs also benefit from monitoring, alerting and response procedures.
Real-life agents might alert you in case of emergency and point to the right exit. Progress ShareFile software also looks out for your safety and possessions. If our teams reach out in such cases, please follow our instructions to hlep mitigate potential risks.
Learn more about how the Progress ShareFile solution is designed for highly regulated industries that need flexible document workflows.
Topics
-
Client Engagement
-
VDR
-
File Management
-
File Sharing
-
Integrated E-signature
-
Apps and Integrations
-
Workflow Automation
-
Security and Compliance
Subscribe to ShareFeed Today
Stay ahead with the latest ShareFile releases, feature enhancements, and product updates delivered monthly straight to your inbox.
Matthias Van Steen works as a Progress ShareFile Sales and Customer Success Engineer for Benelux, France and DACH (and any English speaker who might need him). Belgium born, Matthias now resides in Bulgaria with his wonderful wife and two sons. In his free time (who has that with two kids?) he likes a good beer, a game of bowling or billiards, or just some board games or a good movie. (Lord of the Rings anyone?) He welcomes meeting and collaborating with all, and he is happy to help out with any technical questions regarding ShareFile.
Related Posts